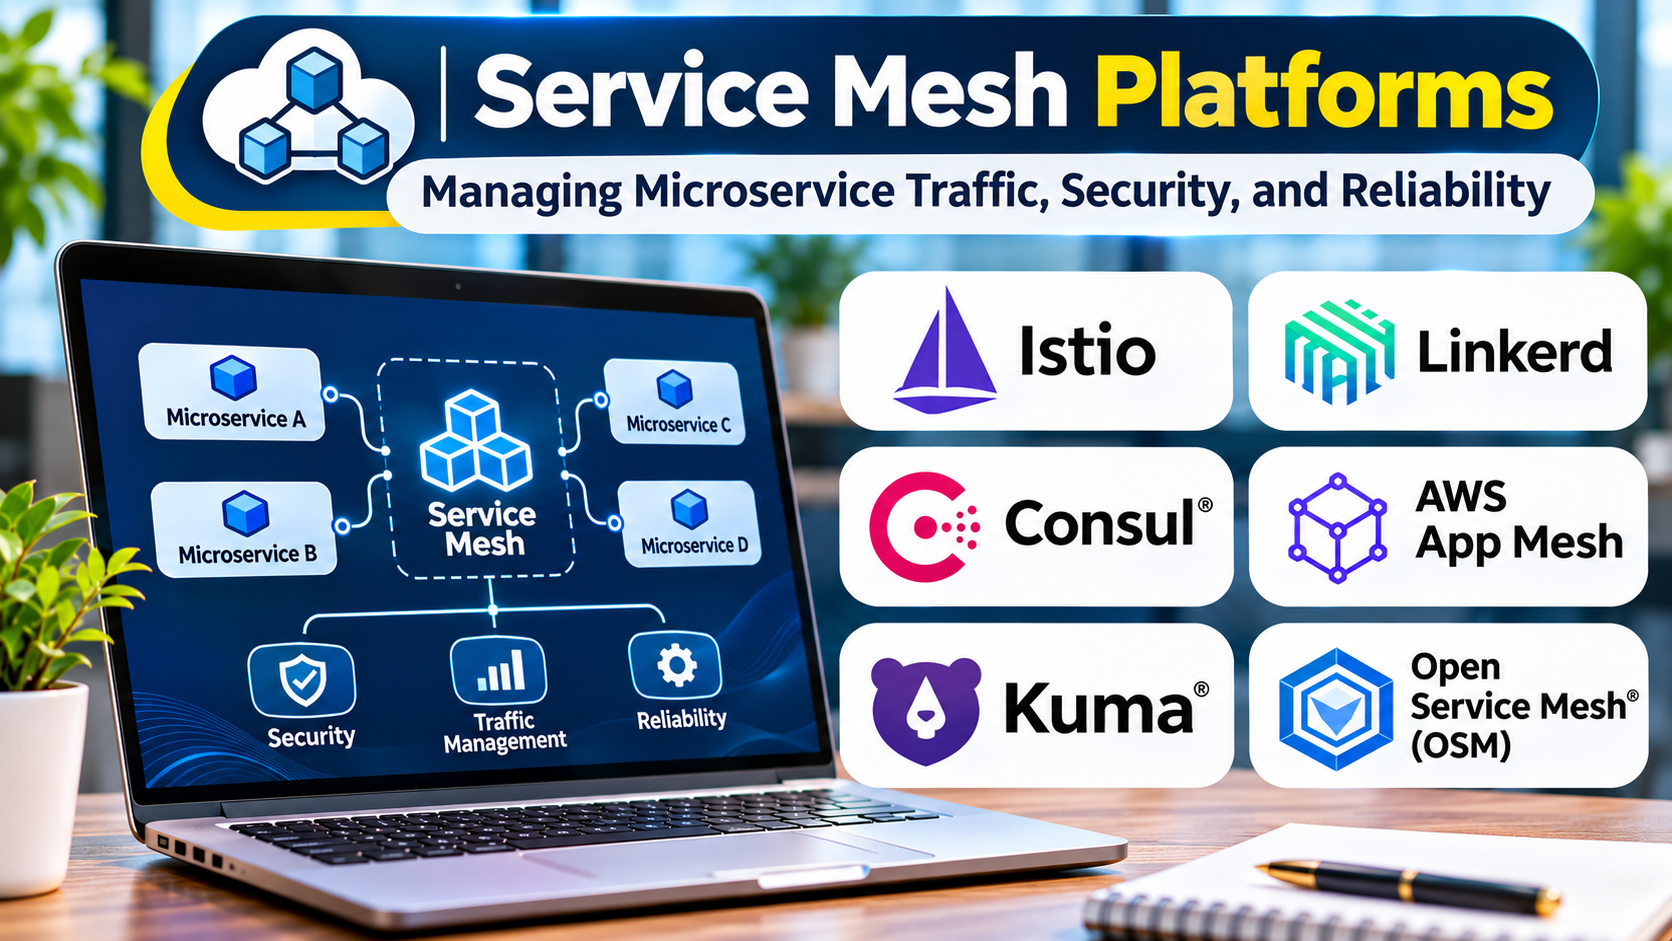
Microservices allow organizations to divide applications into smaller services that can be developed and deployed independently.
This architecture can improve flexibility, but it also creates new operational challenges.
A single business transaction may involve communication between several services. Each connection introduces potential failures, security requirements, and performance concerns.
As the number of services increases, managing communication directly within application code becomes difficult.
Service mesh platforms provide infrastructure-level capabilities for controlling communication between services.
However, a service mesh also introduces additional components and operational overhead.
Understanding when it provides genuine value is essential.
What Is a Service Mesh?
A service mesh is an infrastructure layer that manages communication between services in a distributed application.
It can provide traffic management, service identity, encryption, authorization, and telemetry.
A service mesh commonly separates responsibilities into two areas.
Data plane
The data plane handles service traffic.
Depending on the architecture, it may use proxies deployed alongside workloads or node-level networking components.
These components enforce traffic policies and collect communication metrics.
Control plane
The control plane distributes configuration and manages policies applied by the data plane.
It helps administrators define how services should communicate.
The specific architecture varies by platform.
Why Organizations Use Service Mesh Technology
Service-to-service security
Microservices frequently exchange sensitive information.
A service mesh can support mutual TLS, or mTLS, to authenticate communicating workloads and encrypt traffic.
Traffic management
Organizations may need to direct traffic between different versions of an application.
Service mesh capabilities can support controlled routing, traffic splitting, and other deployment strategies.
Observability
Distributed applications can be difficult to troubleshoot.
A service mesh may provide consistent telemetry about service communication, including request rates, errors, and latency.
Reliability controls
Some service meshes provide timeout, retry, and connection management policies.
These controls can improve resilience when configured appropriately.
However, excessive retries can increase load during failures.
Service Mesh Platforms Worth Evaluating
Istio
Istio is an open-source service mesh project designed to manage service communication.
It provides traffic management, security, and observability capabilities.
Best suited for: Organizations operating complex microservice environments.
Strengths:
- Traffic routing policies
- Mutual TLS capabilities
- Service authorization
- Telemetry integration
- Kubernetes ecosystem support
- Multiple data plane deployment approaches
Considerations: Istio can introduce operational complexity.
Teams should understand its control plane, data plane, resource requirements, and upgrade processes.
Linkerd
Linkerd is an open-source service mesh designed with an emphasis on operational simplicity and Kubernetes environments.
It provides service communication security and observability features.
Best suited for: Kubernetes teams seeking a focused service mesh.
Strengths:
- Kubernetes-oriented design
- Mutual TLS
- Service metrics
- Traffic reliability features
- Lightweight operational approach
Considerations: Organizations should verify whether its traffic management capabilities meet their specific requirements.
Consul
HashiCorp Consul provides service networking and service discovery capabilities.
Its service mesh features support secure communication and connectivity across supported environments.
Best suited for: Organizations managing services across mixed infrastructure.
Strengths:
- Service discovery
- Service identity
- Secure service communication
- Support for varied infrastructure environments
- Integration with HashiCorp technologies
Considerations: Consul has a broader service networking scope than a Kubernetes-only mesh.
Licensing, deployment models, and current feature availability should be verified.
Cilium Service Mesh
Cilium provides cloud-native networking and security capabilities based on eBPF.
Its service mesh capabilities can support service communication and traffic management using supported architectures.
Best suited for: Kubernetes teams seeking integrated networking, security, and service mesh functionality.
Strengths:
- eBPF-based networking
- Network security policies
- Service communication capabilities
- Kubernetes integration
- Observability through associated tooling
Considerations: Organizations should verify which features require specific Kubernetes versions, networking configurations, or deployment modes.
Kuma
Kuma is an open-source service mesh project associated with Kong.
It provides service connectivity and security capabilities across supported environments.
Best suited for: Teams seeking service mesh capabilities across Kubernetes and compatible virtual machine environments.
Strengths:
- Service connectivity management
- Mutual TLS
- Traffic policies
- Multizone architecture
- Support for different infrastructure models
Considerations: Operational requirements depend on deployment architecture and the number of managed services.
Service Mesh Comparison
| Platform | Main focus | Suitable environment | Key consideration |
|---|---|---|---|
| Istio | Advanced service traffic management | Complex microservices | Operational complexity |
| Linkerd | Kubernetes service security | Kubernetes environments | Feature requirements |
| Consul | Service networking and discovery | Mixed infrastructure | Product scope and licensing |
| Cilium | Networking, security, and service mesh | Kubernetes infrastructure | Architecture compatibility |
| Kuma | Cross-environment service mesh | Kubernetes and VM environments | Deployment complexity |
Service Mesh vs. API Gateway
Service meshes and API gateways address related but different communication requirements.
An API gateway commonly manages requests entering an application environment.
It may provide authentication, routing, rate limiting, and API policy enforcement.
A service mesh primarily focuses on communication between internal services.
| Capability | API gateway | Service mesh |
|---|---|---|
| Typical traffic | External-to-internal | Service-to-service |
| API authentication | Common | Depends on architecture |
| Service identity | Possible | Core focus |
| Traffic routing | Common | Common |
| Internal service telemetry | Limited or integration-based | Often integrated |
| API product management | Available in some products | Not primary purpose |
Organizations may use both technologies.
A service mesh does not automatically replace an API gateway.
Important Service Mesh Features
Mutual TLS
Mutual TLS allows communicating workloads to authenticate each other.
It also supports encrypted communication.
Certificate issuance, rotation, and trust management are important implementation details.
Authorization policies
A service mesh can help control which services may communicate.
Policies should follow least-privilege principles.
Traffic splitting
Traffic splitting can direct a percentage of requests to different application versions.
This is useful for controlled rollouts and testing.
Observability
Service-level metrics help administrators investigate communication failures.
However, service mesh telemetry should complement application logs and distributed tracing rather than replace them.
Failure handling
Timeouts, retries, and circuit-breaking mechanisms can help manage failures.
These policies require careful configuration to avoid making incidents worse.
When Does a Service Mesh Make Sense?
A service mesh can be useful when an organization operates many microservices and needs consistent communication policies.
It may be particularly valuable when teams require workload identity, internal encryption, and standardized telemetry.
However, smaller applications may not benefit enough to justify the added infrastructure.
Kubernetes networking, application libraries, and API gateways may already meet their requirements.
Before adopting a service mesh, organizations should identify the specific communication problems it will solve.
How to Evaluate a Service Mesh
Begin with a representative application.
Measure baseline latency, resource consumption, and operational behavior.
Then deploy the service mesh in a controlled environment.
Test service authentication, authorization policies, traffic routing, and failure handling.
Measure the performance overhead introduced by the data plane.
Evaluate how the mesh behaves during control plane failures and upgrades.
Finally, determine whether developers and operators can troubleshoot the system effectively.
A service mesh should improve operational consistency without making failures harder to understand.
Common Service Mesh Mistakes
One mistake is deploying a service mesh before establishing reliable application monitoring.
Another is assuming that mTLS alone provides complete application security.
A service mesh does not eliminate vulnerabilities in application code or authorization logic.
Organizations may also configure retries without considering their impact on overloaded services.
Finally, service mesh adoption should include clear ownership of policies, certificates, and infrastructure upgrades.
Final Thoughts
Service mesh platforms provide valuable capabilities for managing communication between distributed services.
Istio offers extensive traffic management and security features.
Linkerd emphasizes Kubernetes-oriented service connectivity.
Consul supports broader service networking scenarios, while Cilium integrates service mesh capabilities with cloud-native networking.
Kuma provides another option for managing service communication across supported environments.
The best choice depends on application complexity, security requirements, performance expectations, and operational expertise.
A service mesh should be adopted when it makes distributed applications more reliable and manageable—not simply because an application uses microservices.